
Tealium · Enterprise governance
User Management
Designing bulk onboarding and permission architecture across an expanding enterprise product suite.
Governance had not kept pace with the product portfolio.
Tealium’s original user-management system served its core tag-management product. As EventStream, AudienceStream, and DataAccess grew, customers still had to leave those products and enter a visually different application to manage access.
- Granular permissions made a single user slow to configure.
- Training teams sometimes needed to add hundreds of users at once, with no bulk workflow.
- Customers wanted more control than the limited permissions inherited from the original system.
- A future migration path had to account for multiple products and architectures.
Turn repeated decisions into reusable structure.
I revisited feedback from the first release rather than assuming the established flow should simply be reskinned. Interviews revealed that speed and consistency mattered as much as granular control.
Bulk user creation
Inspired by Amazon Web Services, the workflow accepted multiple email addresses at once and applied shared permission sets in one action.
Permission groups
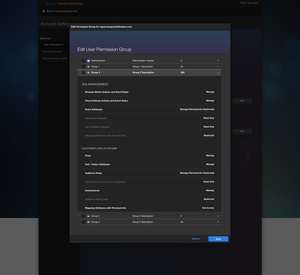
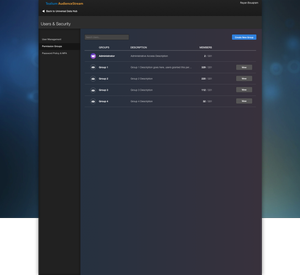
Reusable groups replaced repeated checkbox decisions, making common access patterns easier to assign and explain.
Validation before broad release
I tested an interactive prototype across two rounds, then worked with the team to make the capability available through Early Access.
A sound interaction model still needs an adoption model.
The design earned support and entered development, but the broader account-level vision stalled when executive alignment and migration strategy remained unresolved. The feature was eventually set aside for a later revisit.
The lesson stayed with me: for platform work, the migration story is part of the product—not a conversation to leave until after the interface is designed.